Security3 min read
A recent networking preprint connects integration with a carefully scoped security analysis.
Security3 min read
A product update focuses on the operational side of cryptographic migration.
Security2 min read
The preprint verifies a mathematical argument within explicit device assumptions.
Security2 min read
The final report distinguishes sensitive federal systems from the broader migration timetable.
Security2 min read
The company says SERMA completed the V1 technical evaluation. Site audits and ANSSI certificate issuance remain.
Security2 min read
The partners outline post-quantum work for Indian satellite platforms while leaving deployment schedules to future definition.
Security2 min read
A cryptographic preprint offers a theoretical construction whose security depends on a post-quantum hardness assumption.
Security2 min read
ML-DSA support starts with 1Password 8.12.44. Compatible websites are required and creation still has iOS and native macOS autofill limits.
Security2 min read
Operation FlashHole illustrates an unexpected use for ML-KEM. The vendor’s disclosure concerns malware delivery, with activity evidence dating to July 2025.
Security2 min read
New Database 19c guidance makes client compatibility and the negotiated connection central to the migration.
Security2 min read
The October 22 COINS Act proposal broadens the software discussion within covered transactions. A final rule would set the effective date.
Security2 min read
The workshop lists a paper on side-channel analysis. The public announcement is not evidence of a mathematical break of ML-KEM or an independently validated product claim.
Security3 min read
Cloudflare’s PQC service is in closed beta. Its security boundary concerns where protected keys can be opened, while routing and traffic inspection remain separate controls.
Security2 min read
The partners will study digital-asset custody and security controls. Their agreement does not establish a new policy, a premium reduction or a date for quantum attacks.
Security2 min read
The QSN announcement combines post-quantum cryptography, quantum key distribution and quantum randomness. Each addresses a different part of the security problem.
Security2 min read
Black Kite has announced new third-party risk controls. Observable encryption signals are a starting point, not a complete security verdict.
Security2 min read
A scan of 136,711 app binaries found little detectable post-quantum code. That measures one layer of a connection, with important limits.
Security3 min read
A 20-kilometer fiber experiment tests three-bit waveform generation. Its positive asymptotic key estimate retains the security model and sampling costs.
Security4 min read
A new research release makes signature aggregation a question about the complete proof package and its verification contract.
Security3 min read
The October public release exposes gaps found in an earlier audit. Its inventory, funding and testing findings offer a practical way to read post-quantum readiness claims.
Security3 min read
The October 12 deployment guides connect keys, identities and software verification, while leaving application-level cryptography outside cloud API controls.
Security3 min read
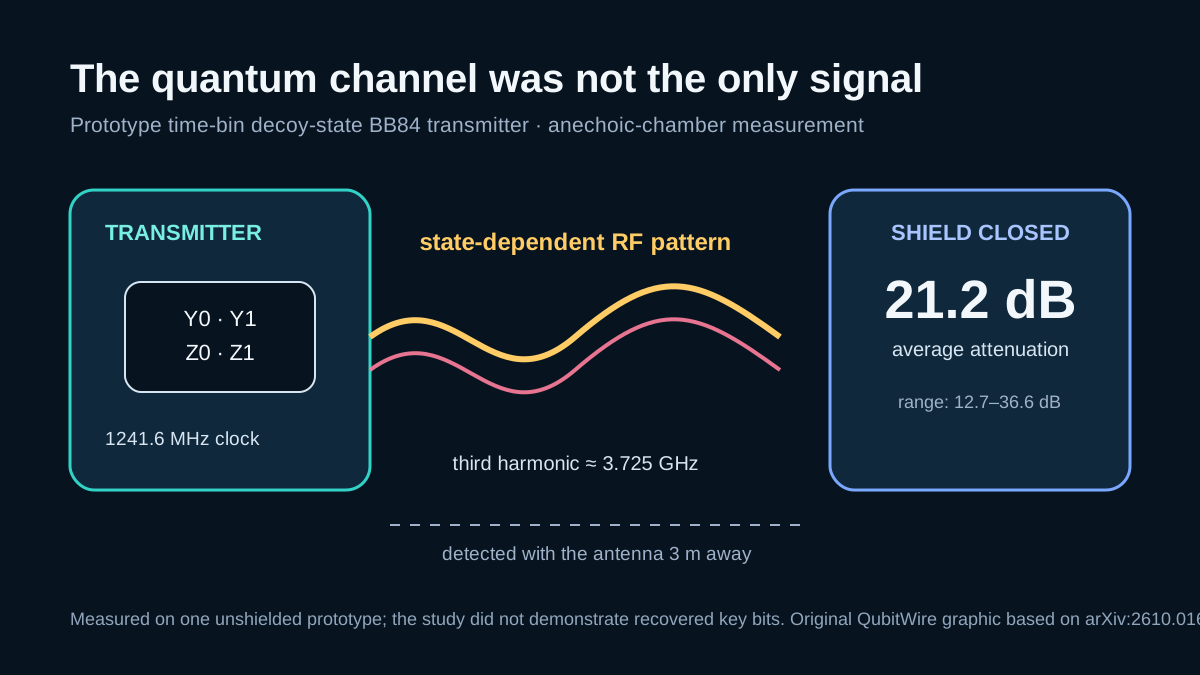
Researchers detected distinct RF patterns from four generated quantum states outside an unshielded prototype. A closed rack cut the measured leakage by 21.2 dB on average.
Security3 min read
A quantum experiment combines light signals and strict timing to test where a device actually is. It is not a replacement for GPS.
Security2 min read
IonQ has put a number on a future cryptographic threat. The machine needed to carry it out does not exist today.