Can light verify a location? NIST tested it across 195 metres
Two stations used timed replies and entangled photons to place a quantum operation inside a target region during at least one trial.
Reading tools for text size, copying, printing and your reading list
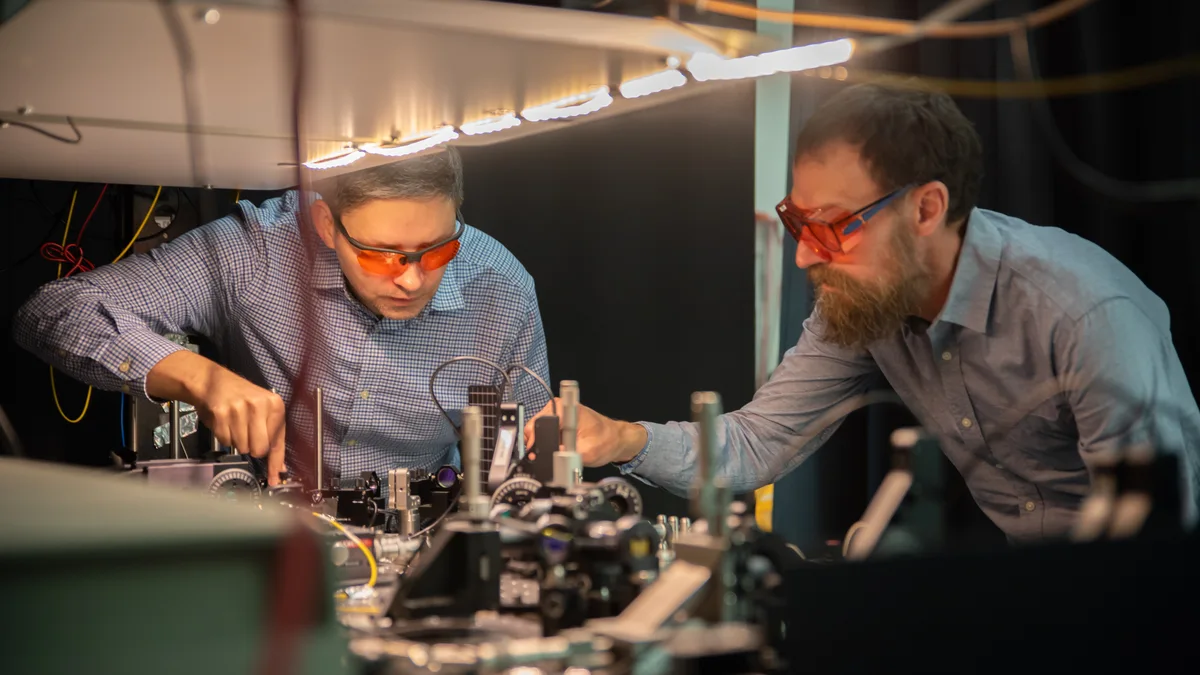
light can help check where a response was produced. NIST researchers demonstrated that idea with two checking stations 195 metres apart in Boulder. The work appears in Nature on November 18.[1]
The distinctive advance is checking location without trusting the internal workings of the quantum equipment. The guarantee still depends on trusted classical timing, distance measurements and secure verifier laboratories, and on limits to attackers’ shared quantum resources. This is a laboratory security experiment, not a location-checking service.[2][3]
A question that has to arrive on time
The stations send random instructions that determine how a photon should be measured. The answer must return promptly enough to fit the claimed location, and repeated measurements must produce the right quantum correlations. Millions of trials build the evidence; a single quick reply is not the test.[1]
The correlations matter because entangled particles do not behave like objects carrying a prearranged list of answers. A Bell test compares their measurement statistics with limits that such local, pre-existing explanations must obey. Carefully separating the measurements and choosing settings unpredictably closes routes to a misleading result. NIST demonstrated a loophole-free Bell test in 2015; the new experiment puts that kind of test to work on a different question: location.[5]
What the experiment actually establishes
The researchers report a localization volume about 4.53 times smaller than a classical protocol with identical delays. That comparison is not a GPS accuracy rating. More precisely, passing certifies that an input-dependent quantum operation occurred inside the target region during at least one trial. It does not establish continuous presence.[2][3]
The implemented protection covers attackers with no or only very weak entanglement shared before each trial; more entanglement can defeat it. Stronger-resource protection belongs to an extended theoretical protocol, not the demonstrated implementation. The data were collected in 2024. A manuscript appeared in January 2026 and was revised in August; November 18 is the journal-publication milestone.[2][3]
Why location is not identity
NIST’s quantum-cryptography explainer makes an important distinction: even successful position verification cannot identify the person behind a device. A future authentication system would need another credential, such as a digital certificate, alongside the location test. A machine inside an approved building and an authorized user are different claims.[4]
Getting quantum links beyond a laboratory is another obstacle. Optical fibres absorb photons, and ordinary copying and amplification cannot preserve arbitrary unknown quantum states. Researchers are developing quantum repeaters that distribute entanglement through shorter links. Those are infrastructure requirements, not something a software update can supply to an ordinary phone.[4]
Two experiments used different rulers
Fan-Yuan and colleagues sent weak light pulses between checking stations two kilometres apart. They reported locating the responder to better than 75 metres under their model, which relies on characterized optical signals and limits on adversaries’ shared resources. Their preprint appeared February 2, 2026 and the paper appeared September 3. The publication dates do not identify the experimental days. QubitWire covered that experiment earlier.[6][7]
The NIST team collected its main data on September 20 and October 7, 2024. The November 18, 2026 publication reports how tightly the observations constrain where an operation happened if the verifiers trust their timing and the adversaries start with little shared entanglement. Its 4.53-fold figure is relative to a classical setup with matching delays. It cannot be compared directly with a distance in metres.[2][3]
NIST estimates practical use may remain more than a decade away. The near-term achievement is experimental evidence for a new way to test physical presence, not an end to phishing.[1]